5 Ways North Korea Gets IT Workers Hired Inside American Companies and the crime story Behind the Laptop Farms
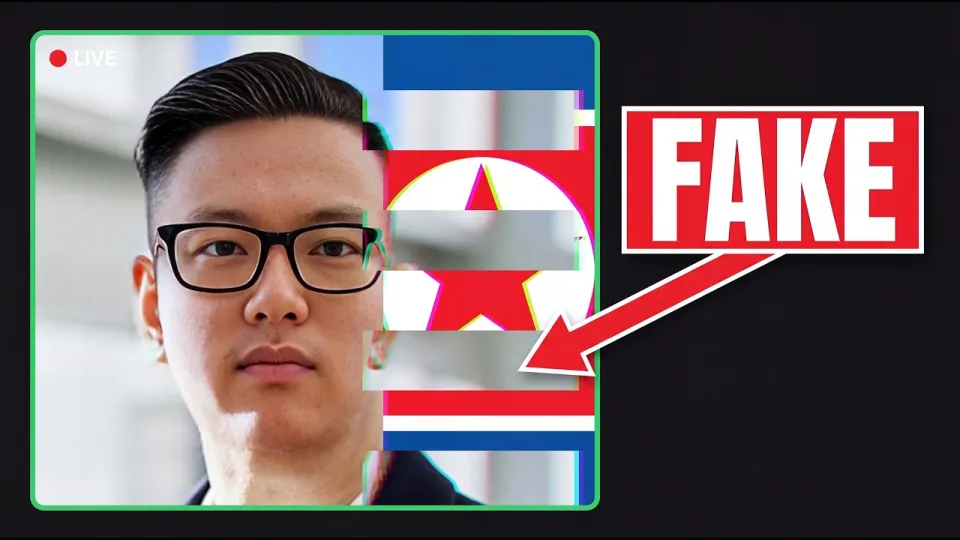
Video: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story)
· based on the channel Max Crime
Key takeaways
- KnowBe4, a security-awareness company, hired a North Korean IT worker who passed four video interviews and a background check before his work laptop began loading malware.
- Christina Chapman of Arizona kept more than 90 laptops on wire shelves in her home, each tagged with a company and a stolen American name.
- Chapman was sentenced to 102 months in federal prison in July 2025; roughly $177,000 stayed with her while more than $17 million moved through her house.
- The FBI and DOJ describe a scheme in which DPRK IT workers use stolen identities, AI-altered photos and remote-access tools to hold US salaries.
- Microsoft Threat Intelligence tracks the related activity as 'Jasper Sleet', and the FBI issued a public service announcement on the threat in January 2025.
North Korea gets its IT workers hired inside American companies by stealing real US identities, passing remote interviews with AI help and routing the work through laptops physically located on American soil. The crime story that best shows this is the case of a security-awareness firm that trained employees to spot fakes and then hired a North Korean operative, and the Arizona woman who hosted more than ninety of the laptops behind such hires.
How the crime story begins with a résumé that looks perfect
The scheme works because the applicant is, on paper, an ordinary American professional. A stolen Social Security number, a real person's name and an AI-touched photo produce a profile that clears automated screening and reference checks. The employer sees an experienced engineer who wants a remote role and asks for nothing unusual.
Four video interviews did not expose the man hired by KnowBe4, a company whose entire business is teaching staff to recognize fraud. The voice on the call, the answers and the credentials held up. Only after the work laptop arrived did the picture change: the machine immediately began loading malware, the kind of software used to reach back into a corporate network from a distance. The device had been shipped to an address that was not the worker's home, and the person on the other end was sitting in North Korea.
3 layers that keep the fake employee invisible
The deception is not one trick but a stack of them, and each layer exists to answer a question a suspicious employer might ask.
- A real identity. Names, dates of birth and identification numbers are taken from US residents, sometimes from people who have no idea their details are circulating. Payroll, tax forms and background checks all resolve to a genuine person.
- A US address and a machine on US soil. Companies ship equipment to American addresses. Someone has to receive the laptop, plug it in and keep it online, because the network connection has to look domestic.
- A remote pipeline into the device. The actual worker connects from abroad through remote-access software, so the keyboard strokes arrive from overseas while the hardware sits in an American home.
This is why the fraud is described as being hired rather than hacked. No firewall was breached to get the job; the company voluntarily granted access to someone it believed it had vetted.
The laptop farm in Arizona and the money that passed through it
Christina Chapman, a US citizen living in Arizona, ran one of the physical nodes of this pipeline. Federal investigators found more than ninety laptops on wire shelving in her home, each one tagged with the name of a company and the stolen identity of the worker it was supposed to belong to. The machines stayed powered and connected so that the people operating them from abroad appeared to be working from an American residence.
Prosecutors said Chapman helped North Korean IT workers obtain jobs at more than 300 US companies, including major retailers and defense-adjacent firms. Her share was about $177,000. More than $17 million in salary payments moved through accounts connected to her house, with the rest of the money flowing onward toward the North Korean regime. She was sentenced to 102 months in federal prison in July 2025. Her defense was that she did not know who she was really working for; prosecutors pointed to her own messages, which they said showed otherwise.
Her case was not isolated. Investigators have described similar setups in other states, including a laptop farm in Texas, and the Justice Department has announced charges and seizures in multiple related schemes, including a June 2025 action that described how the proceeds were funneled.
Why North Korea runs this operation at all
The purpose is foreign currency. Sanctions limit conventional trade, so the regime uses IT workers as a revenue channel: an employee earning a normal American engineering salary sends most of it home, where it funds government programs. Microsoft Threat Intelligence tracks the related infrastructure and tradecraft under the name "Jasper Sleet", and the FBI's Internet Crime Complaint Center issued a public service announcement in January 2025 warning US employers about exactly this pattern.
The workers themselves are often skilled developers, which is part of why they survive technical interviews. They are also frequently organized in teams, with handlers who manage identities, addresses and payments while the developer does the coding. The result is a hybrid crime: identity theft, immigration fraud, money laundering and sanctions evasion, all built around a legitimate employment contract.
Warning signs that show up before the first paycheck
Companies that have caught these hires describe a recognizable cluster of signals rather than a single red flag.
- An applicant insists on a specific shipping address that differs from the résumé, or asks for equipment to be sent to a third party.
- Video interviews are short, audio quality is inconsistent, and the candidate avoids unscripted conversation or asks for questions in advance.
- The photo on the application shows signs of AI manipulation, such as blurred edges around the face or mismatched lighting.
- The candidate's claimed location and the IP address used during onboarding do not match.
- Requests to install remote-access tools or to use a personal virtual machine appear early, framed as productivity preferences.
- Tax and payroll details belong to a person whose history does not line up with the claimed career.
Security teams also recommend verifying identity documents against live video, checking device telemetry after equipment ships, and treating any unexplained outbound connection from a new laptop as an incident rather than an IT glitch.
The night of the alert, minute by minute
When the malware triggered on the newly delivered laptop, the response became a forensic exercise rather than a hiring problem. The timeline that investigators reconstructed runs from 9:55 PM to 10:20 PM: an alert fires, analysts isolate the machine, and within twenty-five minutes they are looking at a device that was never in the hands of the employee it was issued to. The speed matters, because the remote operator on the other end is trying to establish persistence before anyone notices.
The lesson from that evening is that the detection came from the endpoint, not from human resources. The interviews, the background check and the references had all passed. What broke the case open was software behaving like software used by an intruder. Both sides of the story were, in the end, hired: the North Korean developer who took the job under a false name, and the American facilitator who took payment to keep the laptop online.
What the case changes for employers
Remote hiring is now a security decision, not just a recruiting one. Companies are adding address verification, in-person or supervised identity checks, and monitoring of company-issued hardware for remote-access tools. The financial exposure is real: salaries, equipment and, in some cases, access to client systems all flow to a person who may never set foot in the country.
The broader crime story is one of scale. A single house in Arizona supported hundreds of applications, and the money involved ran into the tens of millions. For a full reconstruction of the interviews, the laptop farm and the federal response, see the breakdown by Max Crime, which assembles the Justice Department releases, the FBI warning and the company's own account into a single narrative. The uncomfortable takeaway is that the strongest defense is not better interview questions but better verification of who is actually on the other side of the screen.
Questions & answers
How do North Korean IT workers pass job interviews and background checks?
They use stolen identities of real US residents, so criminal history and employment checks return clean results tied to an actual person. Interviews are conducted remotely, often with AI-assisted video or audio, and handlers coach the candidate on the script. The fraud is designed to survive exactly the checks most companies rely on.
What is a laptop farm and why is it needed?
It is a physical location, often a house, where dozens of company-issued laptops stay powered and connected to American networks. Because the hardware appears to be in the US, the employer's location checks pass while the actual worker operates the machine remotely from abroad. The Arizona case involved more than ninety laptops on wire shelves, each tagged with a company and a stolen name.
How much money does this scheme generate?
In the Arizona case, more than $17 million in salary payments moved through accounts connected to the facilitator's home, while she personally kept about $177,000. Prosecutors said the workers obtained jobs at more than 300 US companies. Most of the remaining money is believed to have been forwarded toward North Korea.
Would a small company notice a fake remote hire?
Possibly not on paper, since the identity and documents are real. Detection usually comes from behavior: an unusual shipping address, remote-access software installed on day one, or device telemetry showing connections from unexpected locations. Companies that monitor issued hardware and verify addresses independently catch these cases far more often than those relying on interviews alone.
Source: Company Has No Idea Its New Hire Is a North Korean Hacker (crime story) · Markdown version